To use an SMB share in a Proxmox LXC container, mount the share on the Proxmox host and pass it into the container as a mount point. That way Jellyfin (or Plex, Nextcloud, qBittorrent) can reach the movies and shows on your NAS, router USB drive or Windows PC. The tricky part is permissions in an unprivileged container: without the right uid and gid the folder shows up empty, owned by nobody, or read-only.
Script card in the catalog: Jellyfin · all Proxmox scripts (RU mirrors / GitFlic).
Tested on Proxmox VE 8 and 9 with Jellyfin installed via the RU Jellyfin script (community-scripts adaptation) or upstream community-scripts. If your Proxmox mini PC also runs your router, see OpenWrt on Proxmox VE. To run your smart home on the same server, see Home Assistant on Proxmox.
How an SMB share works in a Proxmox LXC container
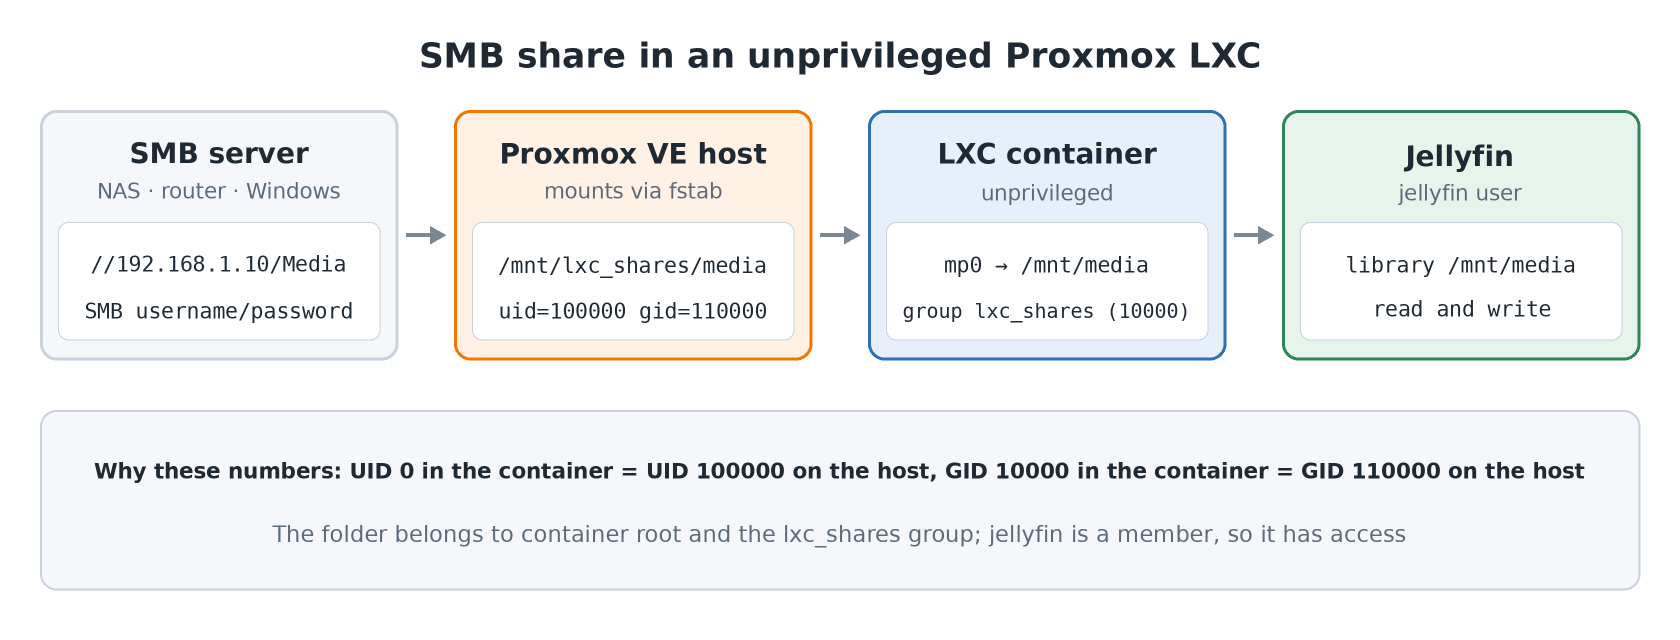
- An unprivileged container cannot mount SMB itself — the kernel does not allow it to mount CIFS. The Proxmox host mounts the share, and the container gets the folder through a bind mount.
- IDs in an unprivileged container are shifted by 100000: container root (UID 0) is UID 100000 on the host, and a group with GID 10000 is GID 110000 (see the Proxmox wiki).
- So the host mounts the share as
uid=100000andgid=110000, and inside the container you create anlxc_sharesgroup with GID 10000 and add thejellyfinuser to it. This approach comes from a well-known Proxmox forum tutorial and works for any number of containers.
What you need
- An SMB share on a NAS, router or computer, with its address, username and password.
- Access to the Proxmox shell: node → Shell in the web UI, or SSH.
- An LXC container running Jellyfin. The examples use ID
102— replace it with yours.
If Jellyfin is not installed yet, the easiest path is the Proxmox scripts catalog (Jellyfin card) or the upstream community-scripts helper — run it in the Proxmox shell:
bash -c "$(curl -fsSL https://raw.githubusercontent.com/community-scripts/ProxmoxVE/main/ct/jellyfin.sh)"The SMB share
How you create it depends on the device. What matters is a user with a password and SMB2 or SMB3 support.
- Router with a USB drive (Keenetic, ASUS, TP-Link and others): enable the file server / SMB sharing, create a user and grant it access to the folder.
- NAS (Synology, TrueNAS, OpenMediaVault): create a shared folder and a user, and enable SMB. Jellyfin only needs read access; Nextcloud or a torrent client needs write access.
- Windows: right-click the drive or folder → Properties → Sharing → Advanced Sharing, tick “Share this folder”, set a name and grant the user access under Permissions.

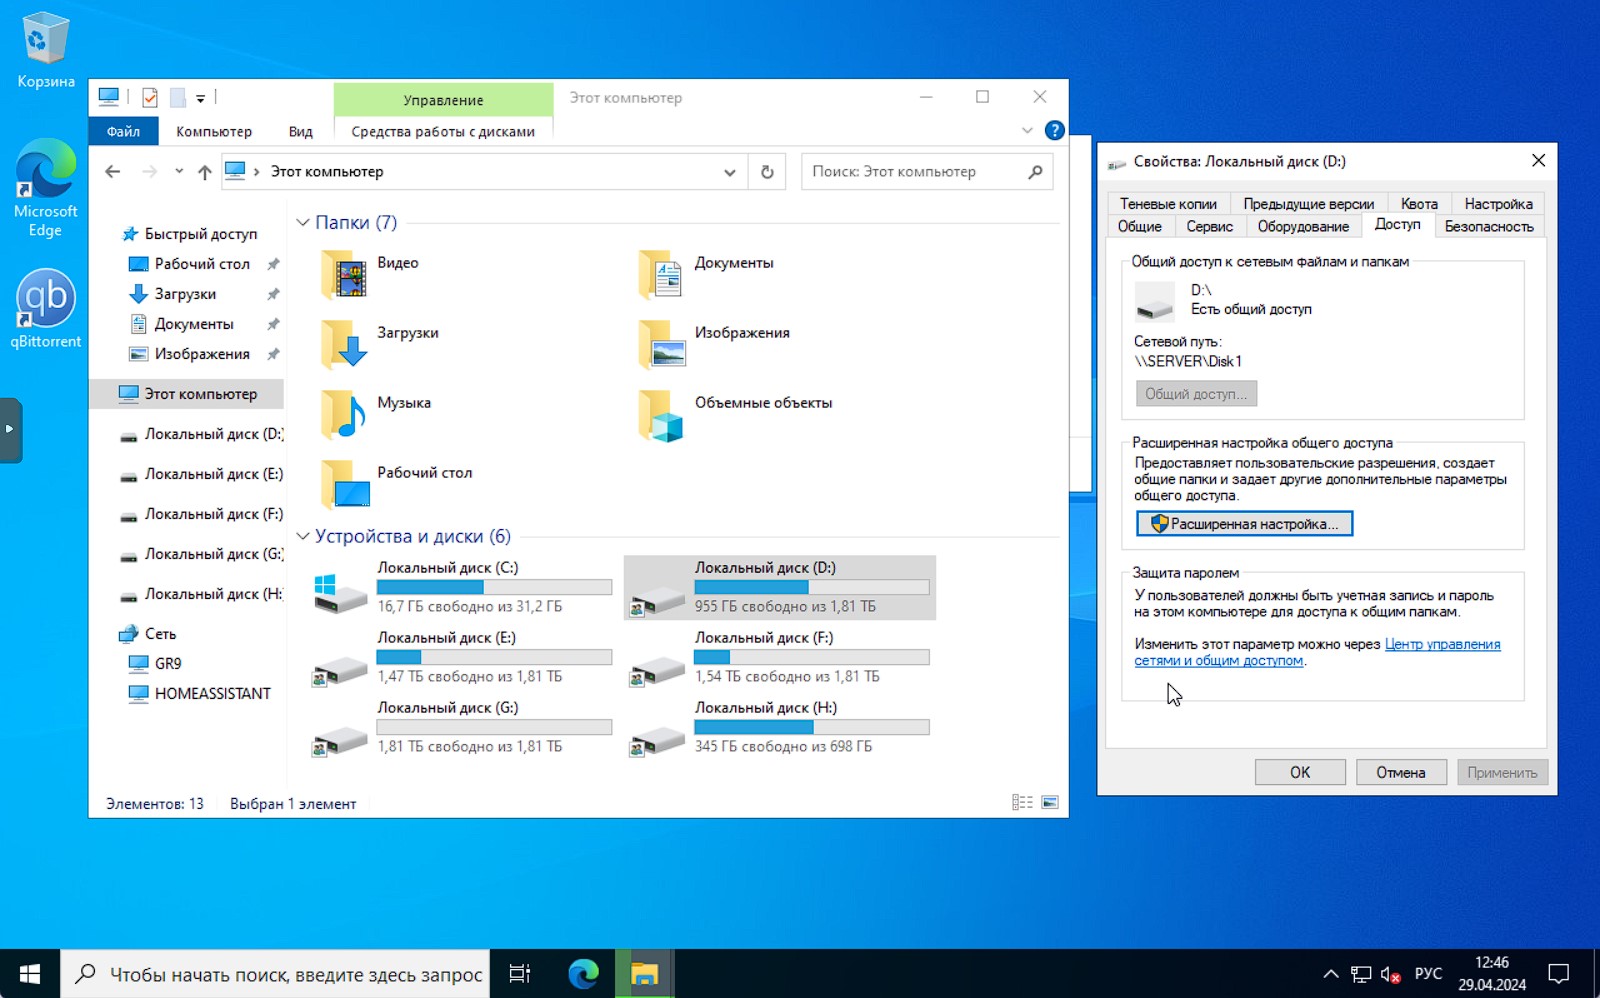
Test access from a PC: open 192.168.1.10Media in File Explorer (use your IP and share name). On Linux and in fstab the same path uses forward slashes: //192.168.1.10/Media.
The lxc_shares group in the container
First create a group with GID 10000 in the container and add the jellyfin user to it. Run these commands in the Proxmox host shell:
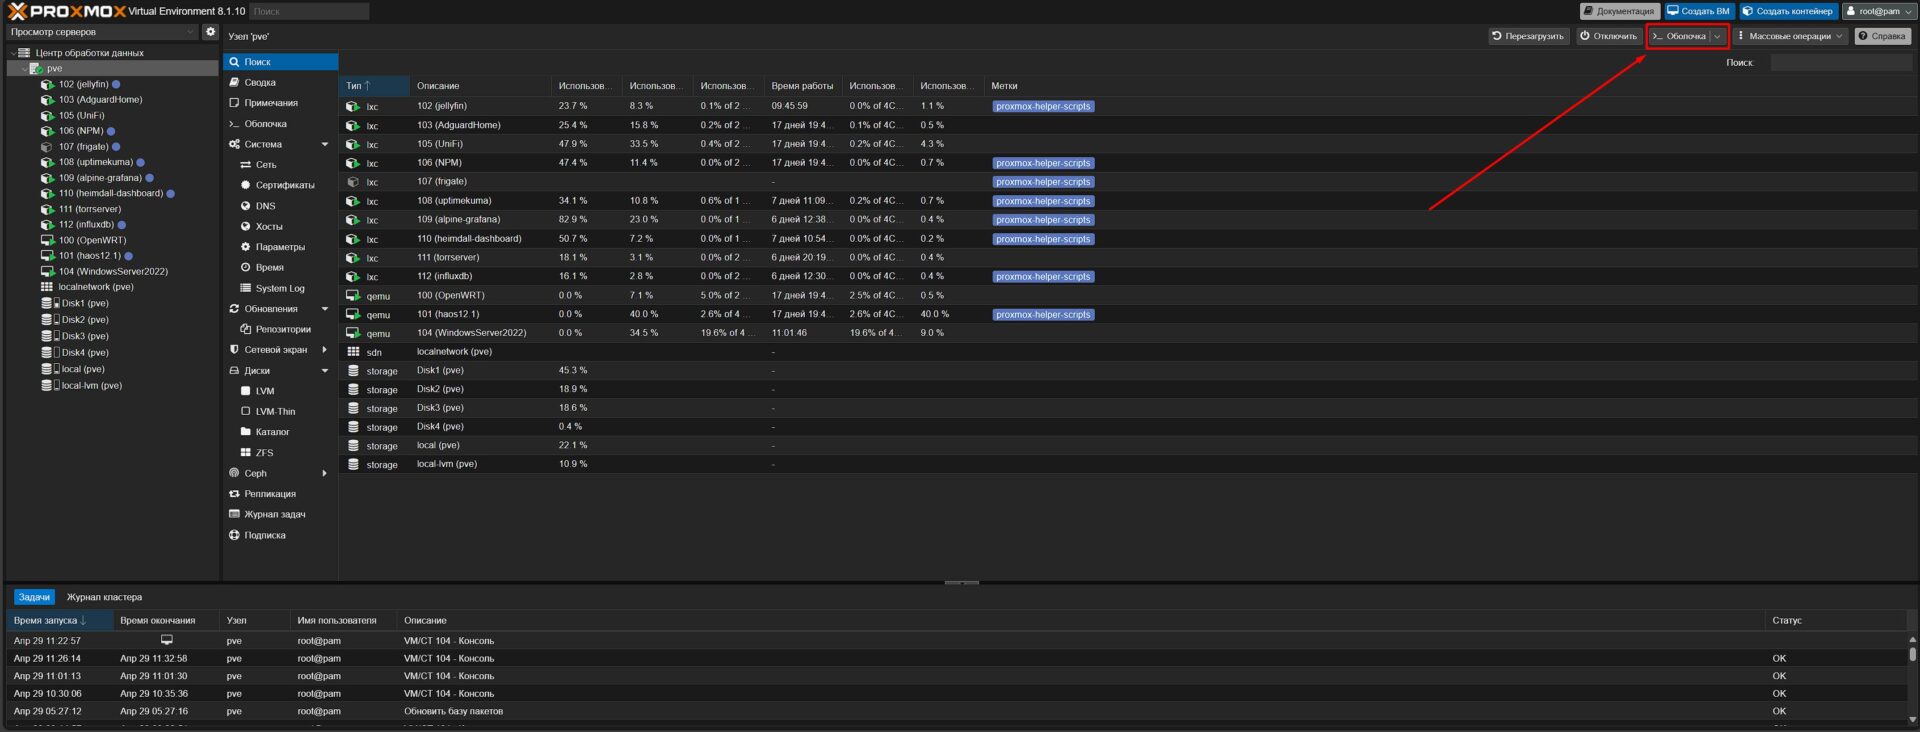
# on the Proxmox host; 102 is your Jellyfin container ID (it must be running)
pct exec 102 -- groupadd -g 10000 lxc_shares
pct exec 102 -- usermod -aG lxc_shares jellyfin
pct shutdown 102
If other applications need the folder too, add their users to the group as well: www-data for Nextcloud, debian-transmission for Transmission, and so on.
Mounting SMB on the Proxmox host
Install the CIFS utilities, create a mount point and a credentials file:
apt install -y cifs-utils
mkdir -p /mnt/lxc_shares/media
nano /root/.smbcredentials
The /root/.smbcredentials file holds two lines with your SMB username and password:
username=smb_user
password=smb_password
# domain=WORKGROUP   # only if the server requires a domain
Save the file (Ctrl+O, Enter, Ctrl+X) and restrict access to it:
chmod 600 /root/.smbcredentialsNow add one line to the end of /etc/fstab (nano /etc/fstab), replacing the address and share name with yours:
//192.168.1.10/Media /mnt/lxc_shares/media cifs _netdev,x-systemd.automount,nofail,noatime,uid=100000,gid=110000,dir_mode=0770,file_mode=0770,credentials=/root/.smbcredentials,iocharset=utf8 0 0uid=100000,gid=110000— on the host the files belong to container root and thelxc_sharesgroup.dir_mode=0770,file_mode=0770— full access for the owner and group, none for others. No need for insecure0777._netdev,x-systemd.automount,nofail— the share is mounted on first access and does not block Proxmox boot if the NAS is off.iocharset=utf8— correct non-ASCII file names.- You do not have to set the protocol version: the client picks the best one (usually SMB 3.1.1). For an old server add
vers=3.0orvers=2.0.
Apply the changes and check the result:
systemctl daemon-reload
mount /mnt/lxc_shares/media

# the owner must be 100000 110000, not root root
ls -ln /mnt/lxc_shares/media | head
Passing the SMB share into the LXC container
Add a mount point and start the container. The command writes an mp0 line to /etc/pve/lxc/102.conf, so there is no need to edit the file by hand:
pct set 102 -mp0 /mnt/lxc_shares/media,mp=/mnt/media
pct start 102
Make sure the files are visible and Jellyfin can write to the folder (it stores artwork and NFO files there if you enable that option):
# the files are visible inside the container
pct exec 102 -- ls -la /mnt/media

# the jellyfin user can write to the folder
pct exec 102 -- su -s /bin/sh jellyfin -c 'touch /mnt/media/.test && rm /mnt/media/.test && echo OK'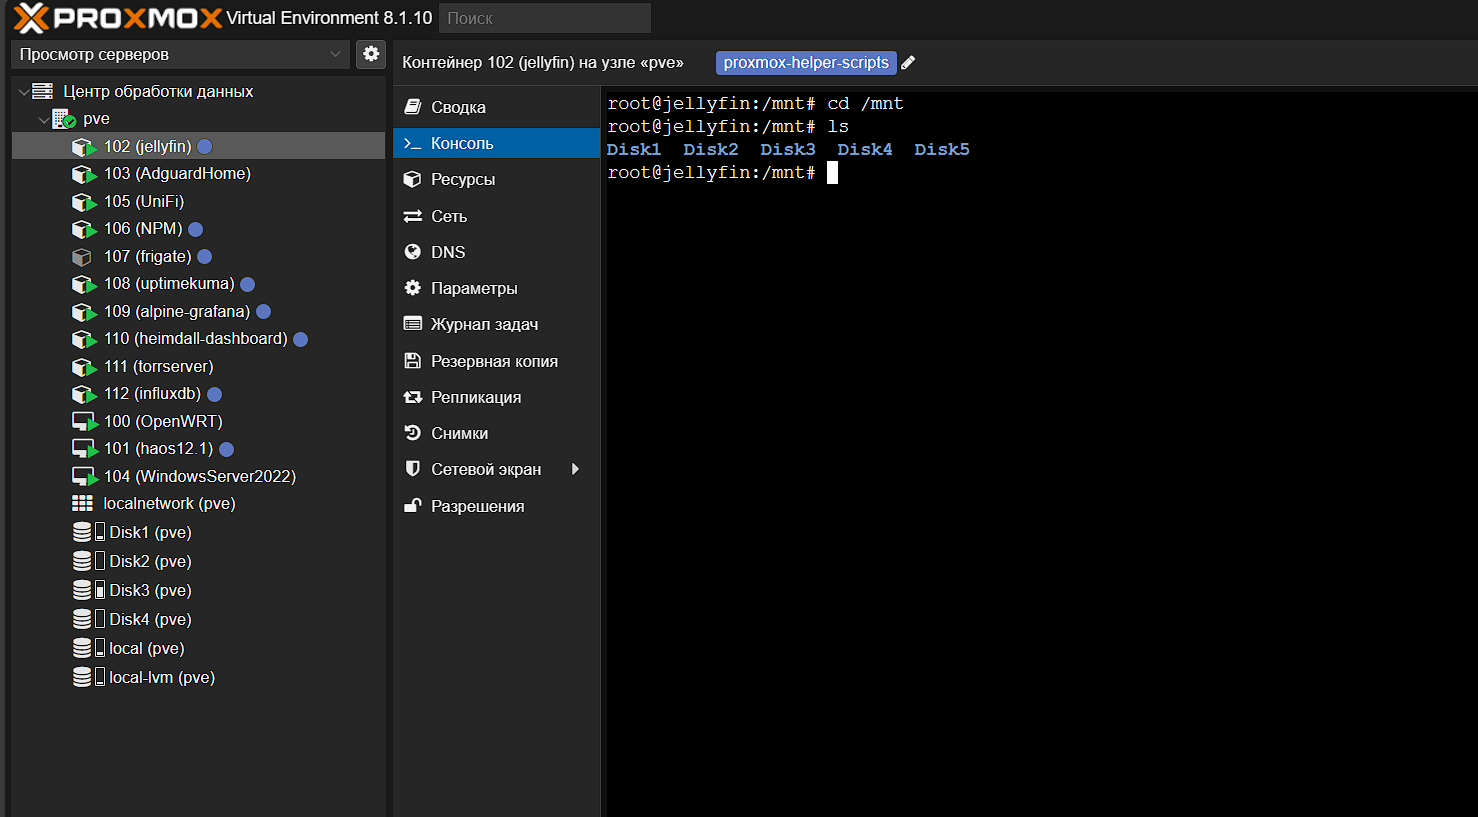
More folders or drives go into mp1, mp2 and so on. The ro=1 option makes a folder read-only, which is handy for music or archives:
mp0: /mnt/lxc_shares/media,mp=/mnt/media
mp1: /mnt/lxc_shares/music,mp=/mnt/music,ro=1
The Proxmox web UI cannot create these mount points: Resources → Add → Mount Point only works with storage volumes, while host folders are passed through with pct set or the config file.
Jellyfin library
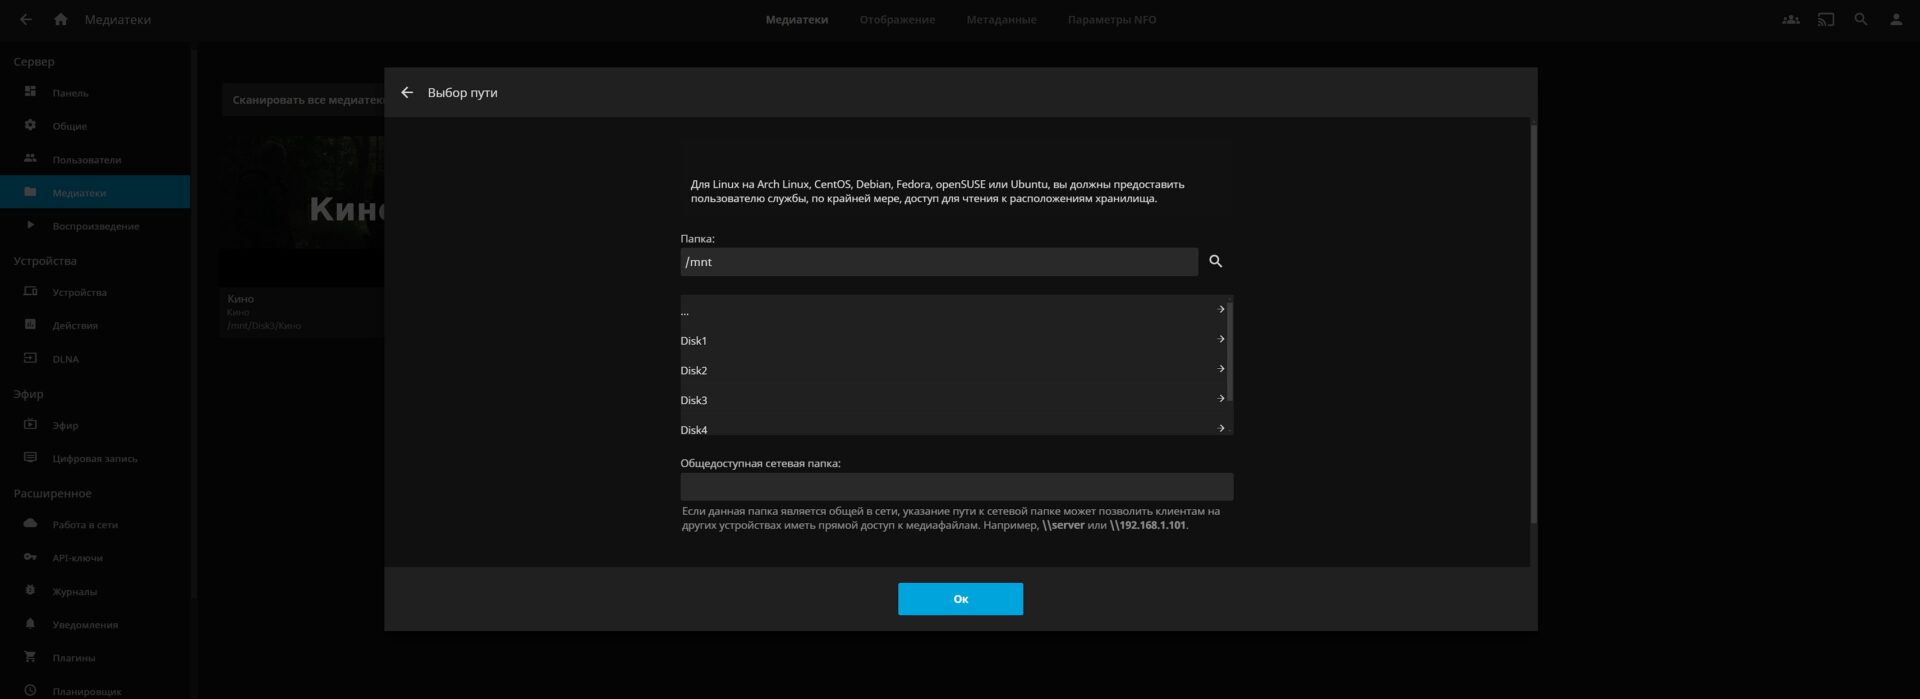
Open the Jellyfin web UI and go to Dashboard → Libraries → Add Media Library. Choose the content type, click “+” next to the folder list and enter /mnt/media (or a subfolder such as /mnt/media/Movies).
Why not use the Proxmox “SMB/CIFS” storage
Proxmox has a built-in SMB/CIFS storage type (Datacenter → Storage → Add → SMB/CIFS). It mounts the share under /mnt/pve/<name>, but as host root. In an unprivileged container those files belong to nobody and are read-only at best. That storage is great for ISO images and backups; for a media library in an LXC, the method in this article works better.
The old approach — mounting the share via fstab and adding it to Proxmox as a “Directory” storage with “Disk image” and “Container” content — is best avoided: Proxmox may place VM disks on the network share, and they become unavailable whenever the NAS goes offline.
Troubleshooting
mount error(13): Permission denied— wrong username or password, the user has no access to the share, or the server requires a domain (adomain=line in the credentials file).mount error(95): Operation not supported— protocol version mismatch. Addvers=3.0, thenvers=2.0tofstab. Routers that only support SMB1 should be updated: that protocol is obsolete and insecure.mount error(112): Host is down— wrong IP, SMB disabled on the server, or the same version issue.mount error(2): No such file or directory— wrong share name.smbclient -Llists the available shares.- The folder is empty in the container — the share is not mounted on the host (
findmnt /mnt/lxc_shares/media) or the container started before the share was mounted. Restart the container; if it happens after every reboot, set a startup delay in Options → Start/Shutdown order. - Files owned by nobody or no write access —
uid=100000,gid=110000is missing, the application user is not inlxc_shares, or the container was not restarted afterwards. - Question marks instead of non-ASCII characters — add
iocharset=utf8. - Proxmox boots slowly when the NAS is off —
fstabis missing_netdev,x-systemd.automount,nofail.
Diagnostic commands:
# which shares the server offers and whether the login works
apt install -y smbclient
smbclient -L //192.168.1.10 -U smb_user

# detailed reason for a mount error
dmesg | grep -i cifs | tail

# is the share mounted on the host
findmnt /mnt/lxc_shares/media
If your Proxmox host is reachable from the internet, cover the basics with the server security checklist. Questions and alternative setups for an SMB share in a Proxmox LXC container are welcome in the comments.
FAQ
Why is the SMB share empty inside a Proxmox LXC container?
Most likely the share is not mounted on the host, or the container started before it. Check u003ccodeu003efindmnt /mnt/lxc_shares/mediau003c/codeu003e on the host, run u003ccodeu003emount /mnt/lxc_shares/mediau003c/codeu003e and restart the container.
Why are files owned by nobody with no write access in the container?
IDs in an unprivileged container are shifted by 100000. Mount the share on the host with u003ccodeu003euid=100000,gid=110000u003c/codeu003e, create an u003ccodeu003elxc_sharesu003c/codeu003e group with GID 10000 in the container and add the application user to it.
Can I mount SMB directly inside an LXC container?
Not in an unprivileged one — the kernel does not allow it to mount CIFS. A privileged container can, but it is less secure. Mounting on the host and using a bind mount is more reliable.
What goes into the SMB credentials file?
Two lines: u003ccodeu003eusername=your_useru003c/codeu003e and u003ccodeu003epassword=your_passwordu003c/codeu003e, plus u003ccodeu003edomain=WORKGROUPu003c/codeu003e if needed. Then run u003ccodeu003echmod 600u003c/codeu003e on the file.
Do I need a username and password for a guest share?
For a guest share, use the u003ccodeu003eguestu003c/codeu003e option in u003ccodeu003efstabu003c/codeu003e instead of u003ccodeu003ecredentials=u003c/codeu003e. A dedicated user is still better: many modern servers and Windows block guest access over SMB2/SMB3.
How do I pass several drives or folders into the container?
Mount each share on the host in its own folder and add mount points u003ccodeu003emp1u003c/codeu003e, u003ccodeu003emp2u003c/codeu003e and so on: u003ccodeu003epct set 102 -mp1 /mnt/lxc_shares/music,mp=/mnt/musicu003c/codeu003e.
Does this work for Plex, Nextcloud or qBittorrent?
Yes. Add the application user to the u003ccodeu003elxc_sharesu003c/codeu003e group — for example u003ccodeu003ewww-datau003c/codeu003e for Nextcloud — and restart the container.
Why not use the SMB/CIFS storage in the Proxmox UI?
It mounts the share as host root, so in an unprivileged container the files belong to nobody. That storage is handy for ISO images and backups; for a media library, an fstab mount with uid and gid works better.
No email, no trackers — just the update feed.